


Microweber is a drag and drop website builder and a powerful next-generation CMS. It's based on the PHP Laravel Framework. You can use Microweber to make any kind of website, online store, and blog. The drag and drop technology allows you to build your website without any technical knowledge.
The core idea of the software is to let you create your own website, online shop or blog. From this moment of creation, your journey towards success begins. Supporting you along the way will be different modules, customizations, and features of the CMS. Many of them are specifically tailored for e-commerce enthusiasts and bloggers.
The most important thing you need to know is that Microweber pairs the latest drag and drop technology, with a revolutionary Real-Time Text Writing and Editing feature. This pair of features deliver improved user experience, easier and quicker content management, a visually appealing environment, and flexibility.
This tutorial will show you how to install Microweber on a fresh FreeBSD 12 system with Nginx as a web server and MariaDB as a database engine.
Requirements
Requirements for installing and running Microweber are as follows:
- PHP version 5.4 or higher with the following PHP extensions: gd2, mcrypt, xml, dom, json
- Web server software like Nginx or Apache.
- MySQL version 5.0 or higher or MariaDB equivalent.
- Composer.
Prerequisites
- FreeBSD 12 operating system.
- A non-root user with
sudoprivileges.
I will be using the domain name example.com in this tutorial. Please replace the word example.com with your own domain name wherever it occurs in the commands and config files below (especially in the Nginx config file and the Let's encrypt commands).
Initial steps
Check your FreeBSD version:
uname -ro
# FreeBSD 12.1-RELEASE
Set up the timezone:
tzsetup
Update your operating system packages (software). This is an important first step because it ensures you have the latest updates and security fixes for your operating system's default software packages:
freebsd-update fetch install
pkg update && pkg upgrade -y
Install some essential packages that are necessary for basic administration of FreeBSD 12.0 operating system:
pkg install -y sudo vim unzip wget bash socatStep 1 - Install PHP and necessary PHP extensions
Microweber web application requires PHP version 5.4 or higher. We can easily install newer PHP by using pkg package manager on FreeBSD 12.
Install PHP, as well as the necessary PHP extensions:
sudo pkg install -y php72 php72-mbstring php72-tokenizer php72-pdo php72-pdo_mysql php72-openssl php72-hash php72-json php72-phar php72-filter php72-zlib php72-dom php72-xml php72-xmlwriter php72-xmlreader php72-curl php72-session php72-ctype php72-iconv php72-gd php72-simplexml php72-zip php72-filter php72-tokenizer php72-calendar php72-fileinfo php72-intl php72-phar php72-soap php72-xmlrpc
To show PHP compiled in modules, you can run:
php -m

ctype
curl
exif
fileinfo
. . .
. . .
Check the PHP version:
php --version

# PHP 7.2.16 (cli) (built: Apr 30 2019 08:37:17) ( NTS )
# Copyright (c) 1997-2018 The PHP Group
# Zend Engine v3.3.5, Copyright (c) 1998-2018 Zend Technologies
# with Zend OPcache v7.3.5, Copyright (c) 1999-2018, by Zend Technologies
Start and enable PHP-FPM service:
sudo sysrc php_fpm_enable=yes
sudo service php-fpm start
We can move on to the next step where we will install acme.sh client and obtain SSL certs.
Step 2 - Install acme.sh client and obtain Let's Encrypt certificate ( optional )
Securing your site with HTTPS is not necessary, but it is a good practice to secure your site traffic. To obtain a TLS certificate from Let's Encrypt we will use acme.sh client. Acme.sh is a simple UNIX shell software for obtaining TLS certificates from Let's Encrypt with zero dependencies.
Download and install acme.sh:
sudo pkg install -y acme.sh
Check acme.sh version:
acme.sh --version
# v2.8.2
Obtain RSA and ECC/ECDSA certificates for your domain/hostname:
# RSA 2048
acme.sh --issue --standalone -d example.com --keylength 2048
# ECDSA
acme.sh --issue --standalone -d example.com --keylength ec-256
If you want fake certificates for testing, you can add
--staging flag to the above commands.
After running the above commands, your certificates and keys will be in:
- For RSA:
/home/username/example.comdirectory. - For ECC/ECDSA:
/home/username/example.com_eccdirectory.
To list your issued certs you can run:
acme.sh --list
Create a directory to store your certs. We will use the
/etc/letsencrypt directory.mkdir -p /etc/letsecnrypt/example.comsudo mkdir -p /etc/letsencrypt/example.com_ecc
Install/copy certificates to /etc/letsencrypt directory.
# RSA
acme.sh --install-cert -d example.com --cert-file /etc/letsencrypt/example.com/cert.pem --key-file /etc/letsencrypt/example.com/private.key --fullchain-file /etc/letsencrypt/example.com/fullchain.pem --reloadcmd "sudo systemctl reload nginx.service"
# ECC/ECDSA
acme.sh --install-cert -d example.com --ecc --cert-file /etc/letsencrypt/example.com_ecc/cert.pem --key-file /etc/letsencrypt/example.com_ecc/private.key --fullchain-file /etc/letsencrypt/example.com_ecc/fullchain.pem --reloadcmd "sudo systemctl reload nginx.service"
All the certificates will be automatically renewed every 60 days.
After obtaining certs exit from root user and return to regular sudo user:
exitStep 3 - Install MariaDB and create a database
Install MariaDB database server:
sudo pkg install -y mariadb102-client mariadb102-server
Check the MariaDB version:
mysql --version
# mysql  Ver 15.1 Distrib 10.2.23-MariaDB, for Linux (x86_64) using readline 5.1
Start and enable MariaDB service:
sudo sysrc mysql_enable="yes"
sudo service mysql-server start
Run
mysql_secure installation script to improve MariaDB security and set the password for MariaDB root user:sudo mysql_secure_installation
Answer each of the questions:
Would you like to setup VALIDATE PASSWORD plugin? N
New password: your_secure_password
Re-enter new password: your_secure_password
Remove anonymous users? [Y/n] Y
Disallow root login remotely? [Y/n] Y
Remove test database and access to it? [Y/n] Y
Reload privilege tables now? [Y/n] Y
Connect to MariaDB shell as the root user:
sudo mysql -u root -p
# Enter password
Create an empty MariaDB database and user for Microweber and remember the credentials:
mysql> CREATE DATABASE dbname;
mysql> GRANT ALL ON dbname.* TO 'username' IDENTIFIED BY 'password';
mysql> FLUSH PRIVILEGES;
Exit from MariaDB:
mysql> exit
Replace
dbname, username and password with your own names.Step 4 - Install and configure NGINX
Install the NGINX web server:
sudo pkg install -y nginx
Check the NGINX version:
nginx -v
# nginx version: nginx/1.14.2
Start and enable NGINX service:
sudo sysrc nginx_enable=yes
sudo service nginx start
Configure Nginx for Microweber by running:
sudo vim /usr/local/etc/nginx/microweber.conf
And populate the file with the following configuration:
server {
  listen 80;
  listen 443 ssl;

  server_name example.com;
  root /usr/local/www/microweber;

  # RSA
  ssl_certificate /etc/letsencrypt/example.com/fullchain.pem;
  ssl_certificate_key /etc/letsencrypt/example.com/private.key;
  # ECC
  ssl_certificate /etc/letsencrypt/example.com_ecc/fullchain.pem;
  ssl_certificate_key /etc/letsencrypt/example.com_ecc/private.key;

  index index.php;

  location / {
    try_files $uri $uri/ /index.php$is_args$args;
  }

  location ~ \.php$ {
    try_files $uri =404;
    include fastcgi_params;
    fastcgi_index index.php;
    fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
    fastcgi_pass 127.0.0.1:9000;
  }
}
Run
sudo vim /usr/local/etc/nginx/nginx.conf and add the below line to http {} block to include Microweber config.include microweber.conf;
Check Nginx configuration for syntax errors:
sudo nginx -t
Reload Nginx service:
sudo service nginx reloadStep 5 - Install Microweber
Create a document root directory where Microweber should reside in:
sudo mkdir -p /usr/local/www/microweber
Navigate to the document root directory:
cd /usr/local/www/microweber
Download the latest version of Microweber CMS and unzip it:
sudo wget https://download.microweberapi.com/ready/core/microweber-latest.zip
sudo unzip microweber-latest.zip
sudo rm microweber-latest.zip
Change ownership of the
/usr/local/www/microweber directory to www:sudo chown -R www:www /usr/local/www/microweber
Open your domain name (
http://example.com/) in your web browser and follow the instructions. After installation, your admin panel URL will be at http://example.com/admin.Step 6 - Finish the Microweber installation
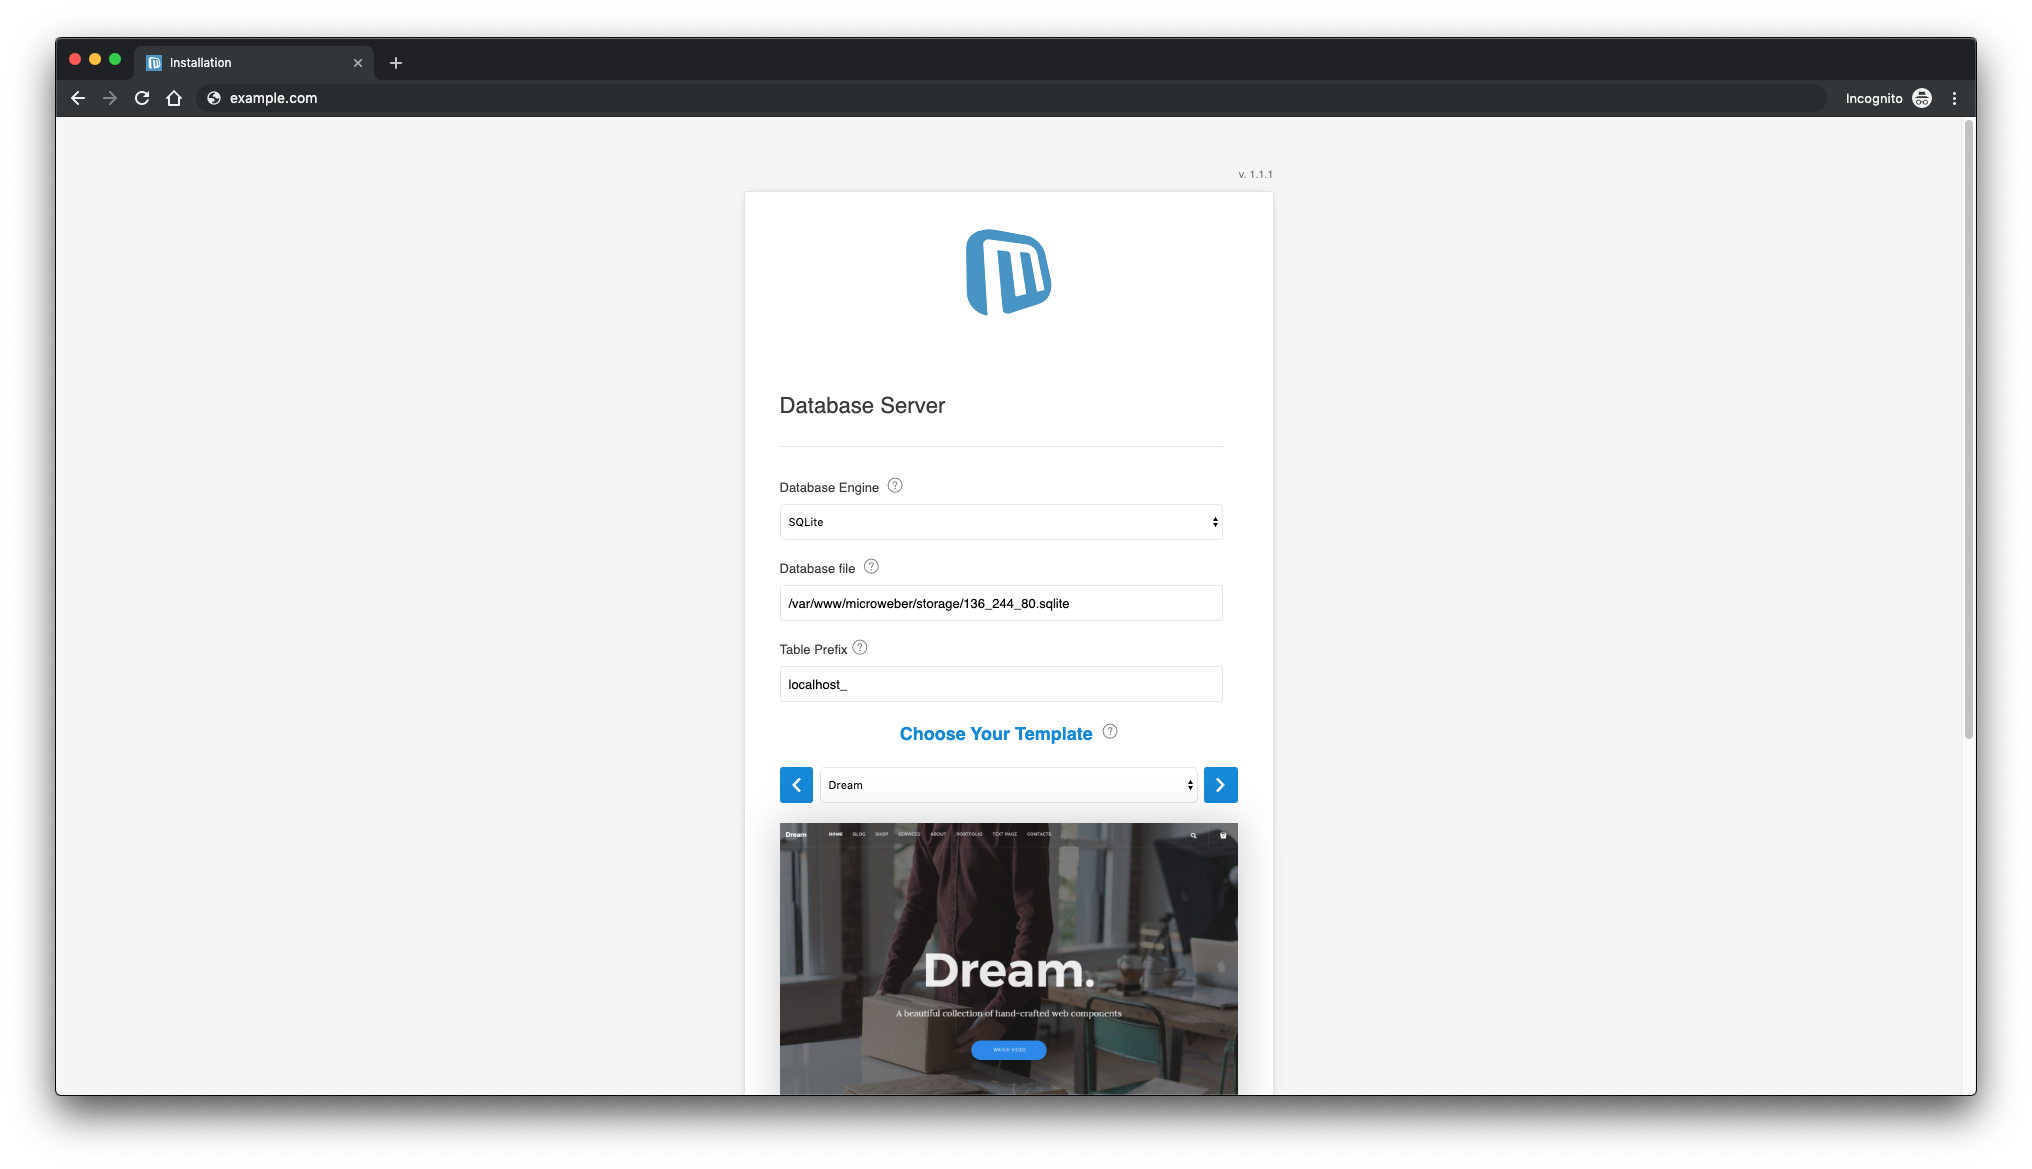
Open your web browser and type the URL http://example.com. You will be redirected to the following page where you will need to choose the database engine of your choice. This tutorial uses MySQL/MariaDB. You can select SQLite like the screenshot below shows:
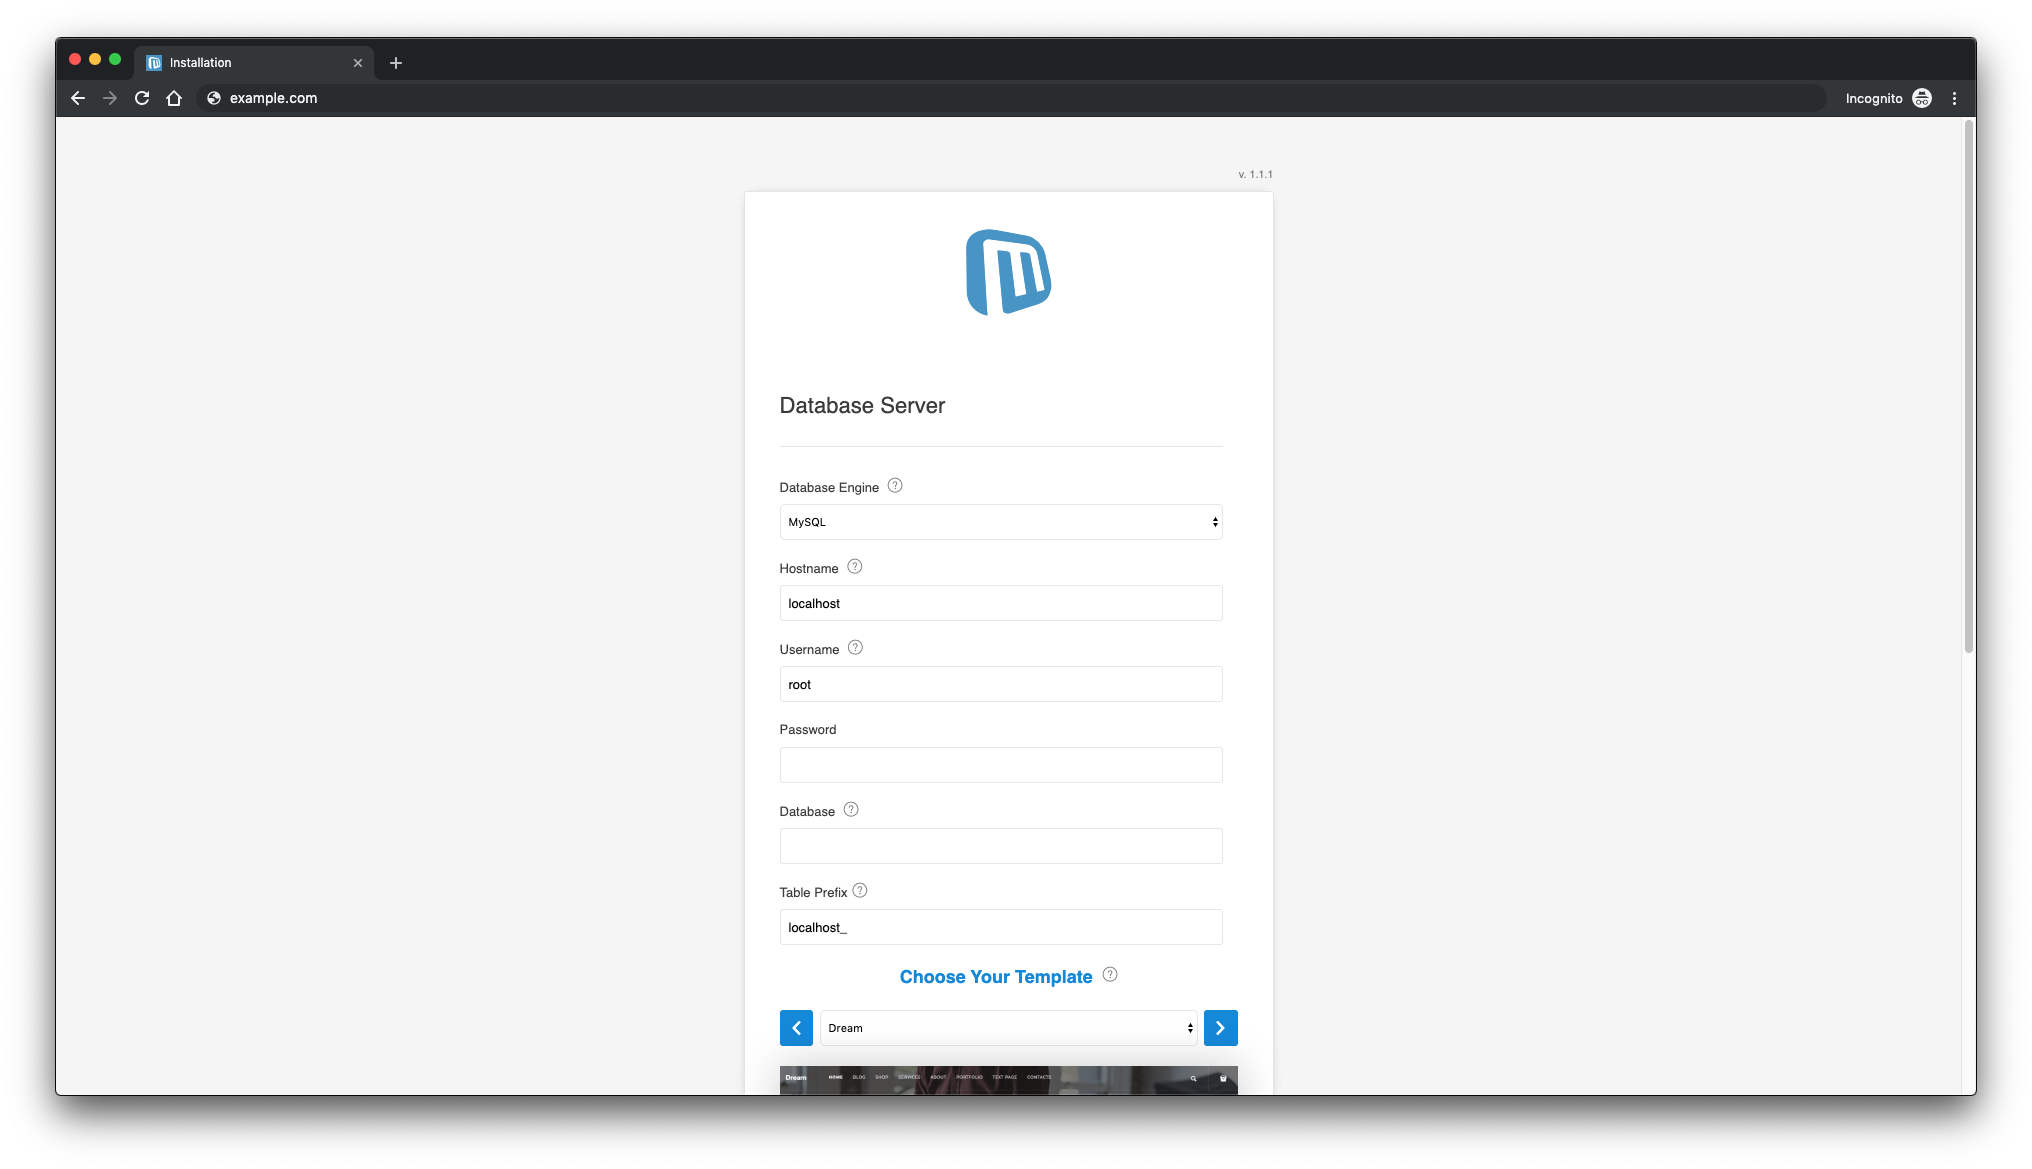
You can select the MySQL database engine:
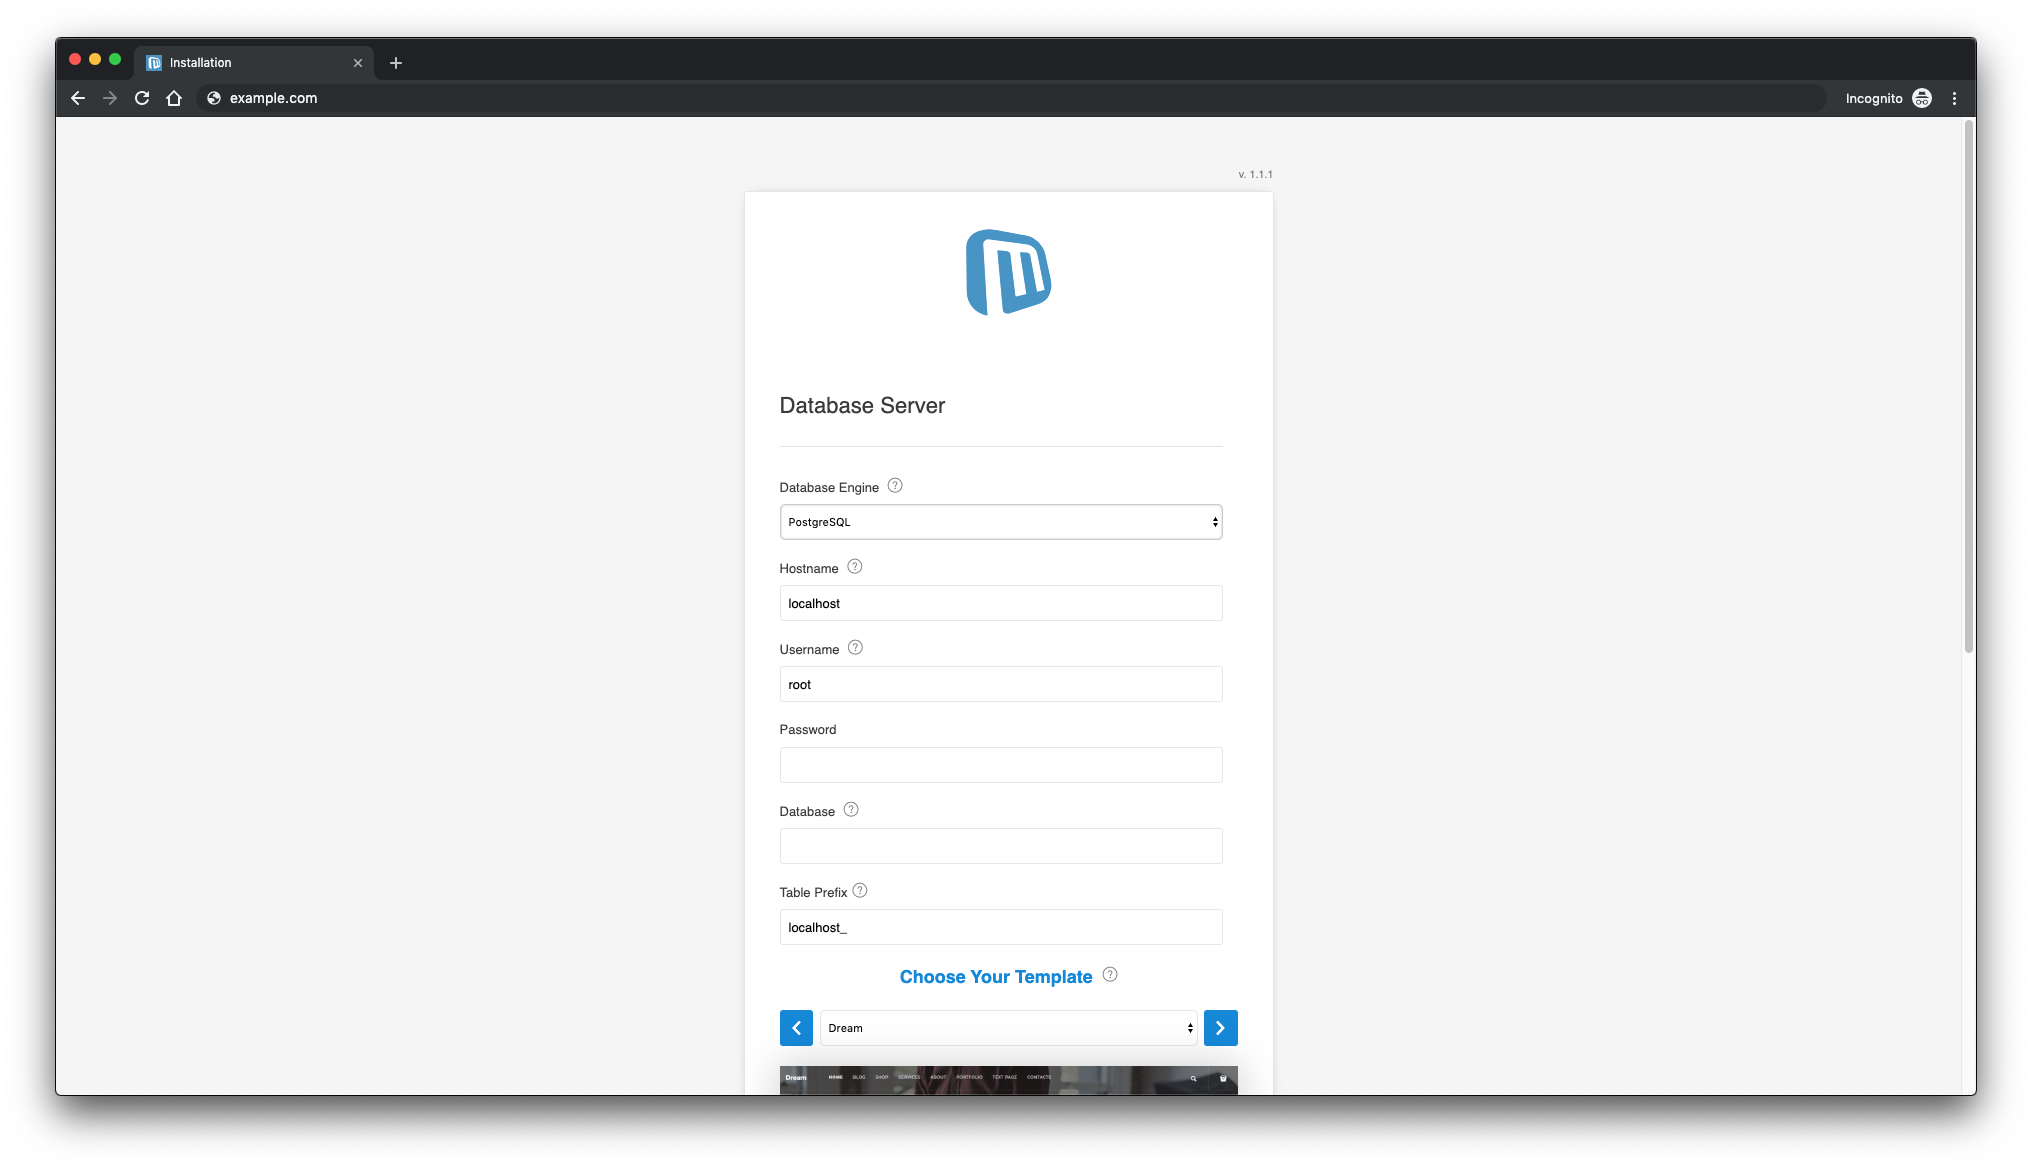
Or PostgreSQL if you prefer it:
After entering the requested details Microweber installation is completed. To access Microweber admin append /admin to your website URL.
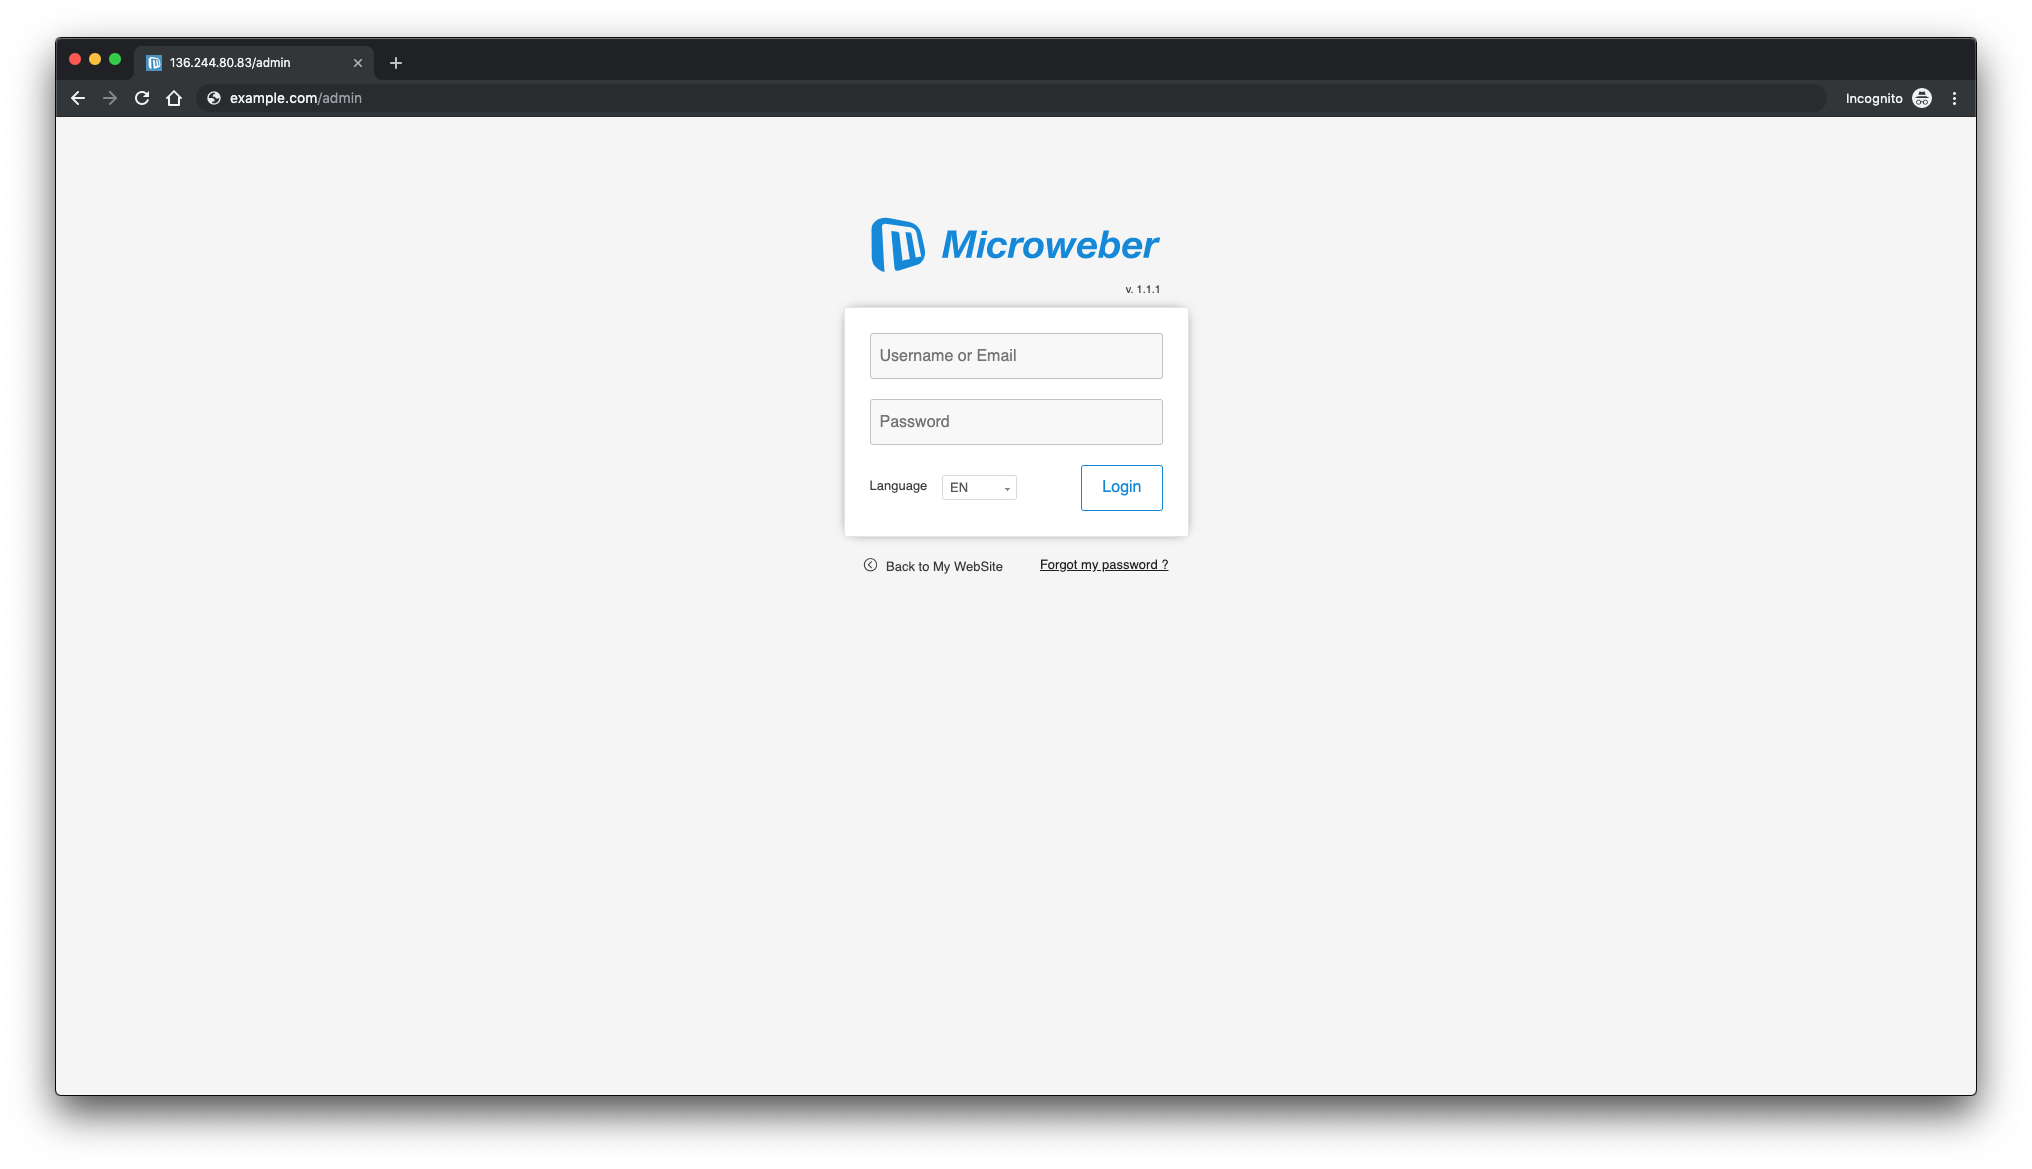
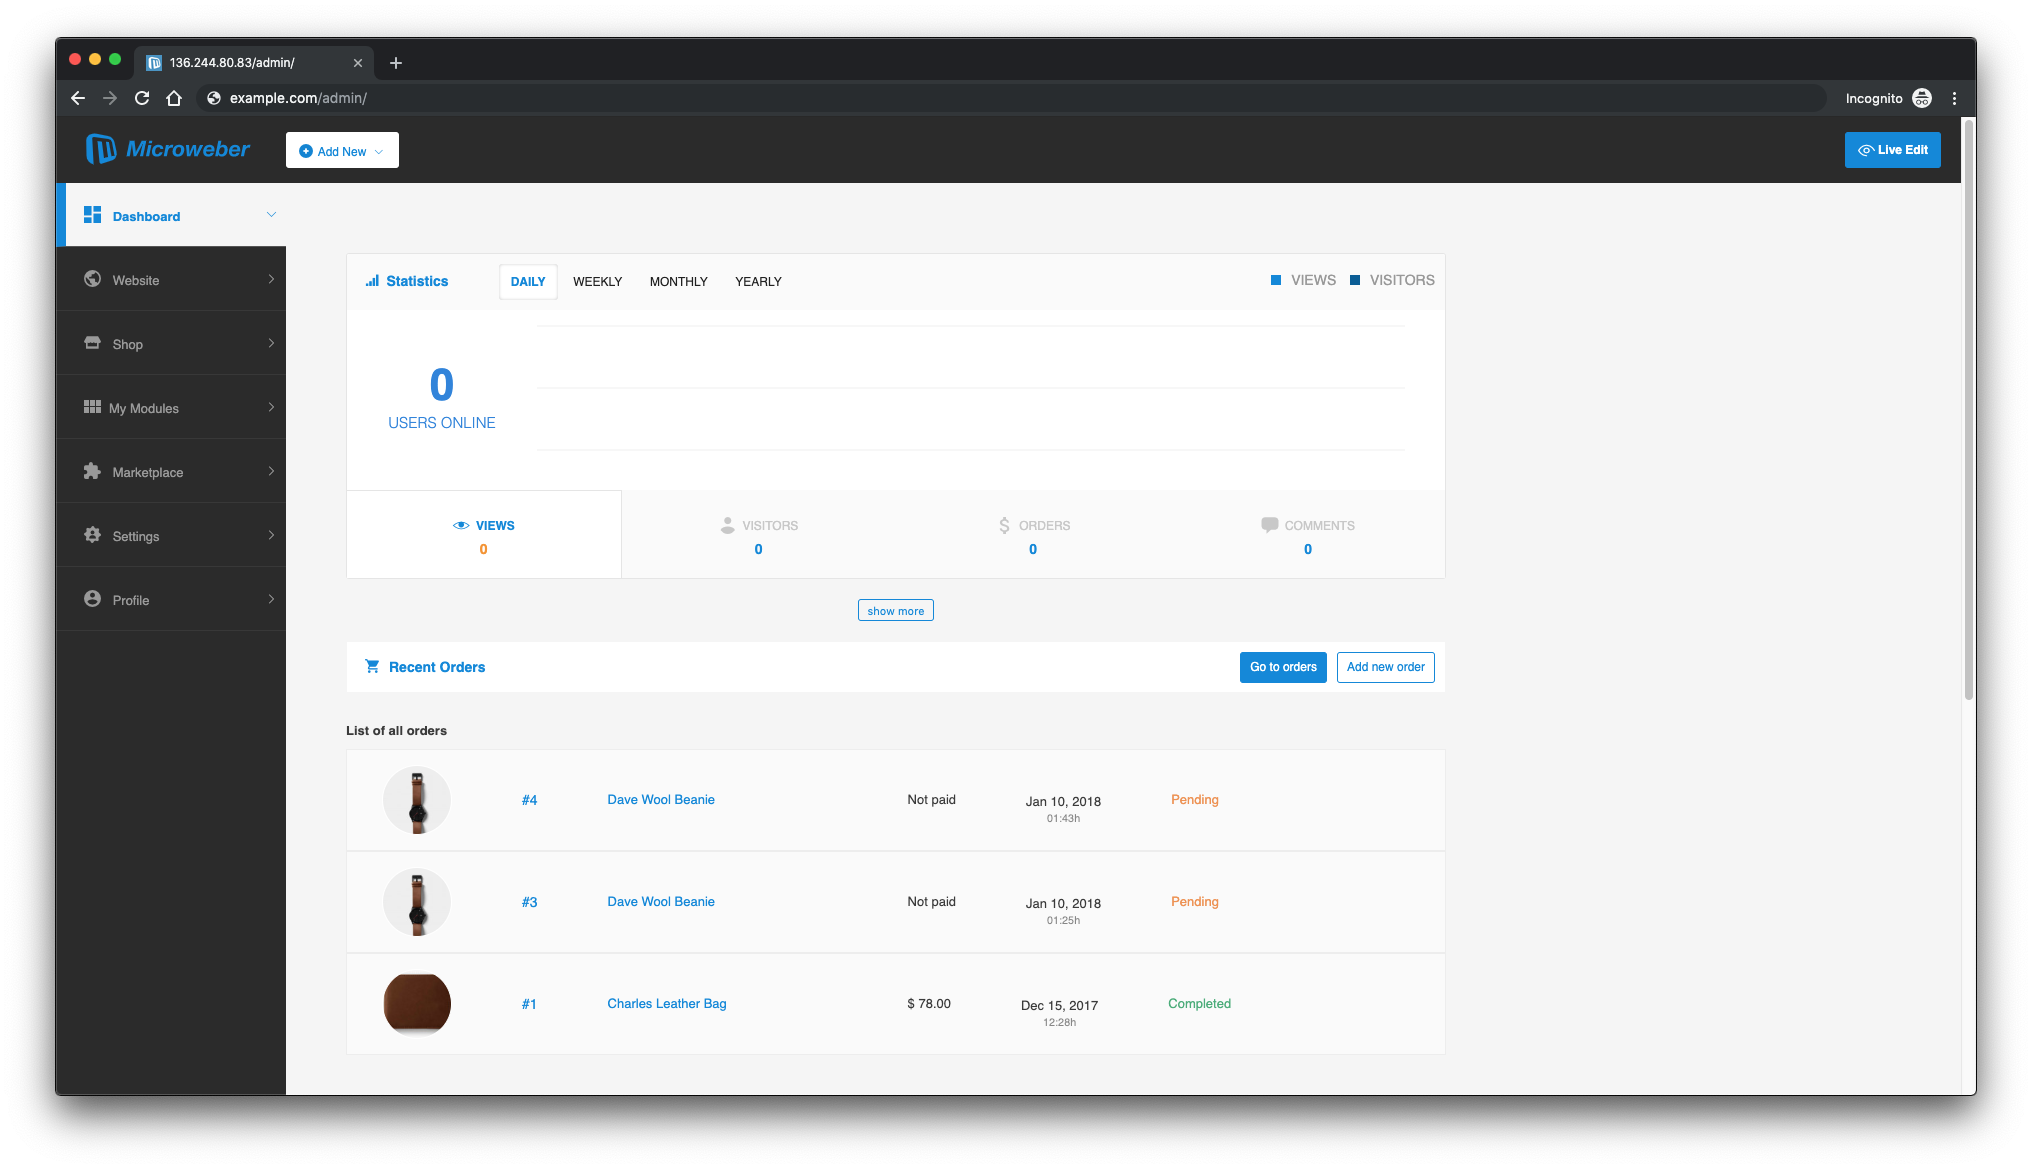
After login, here is how the Microweber dashboard will look like:
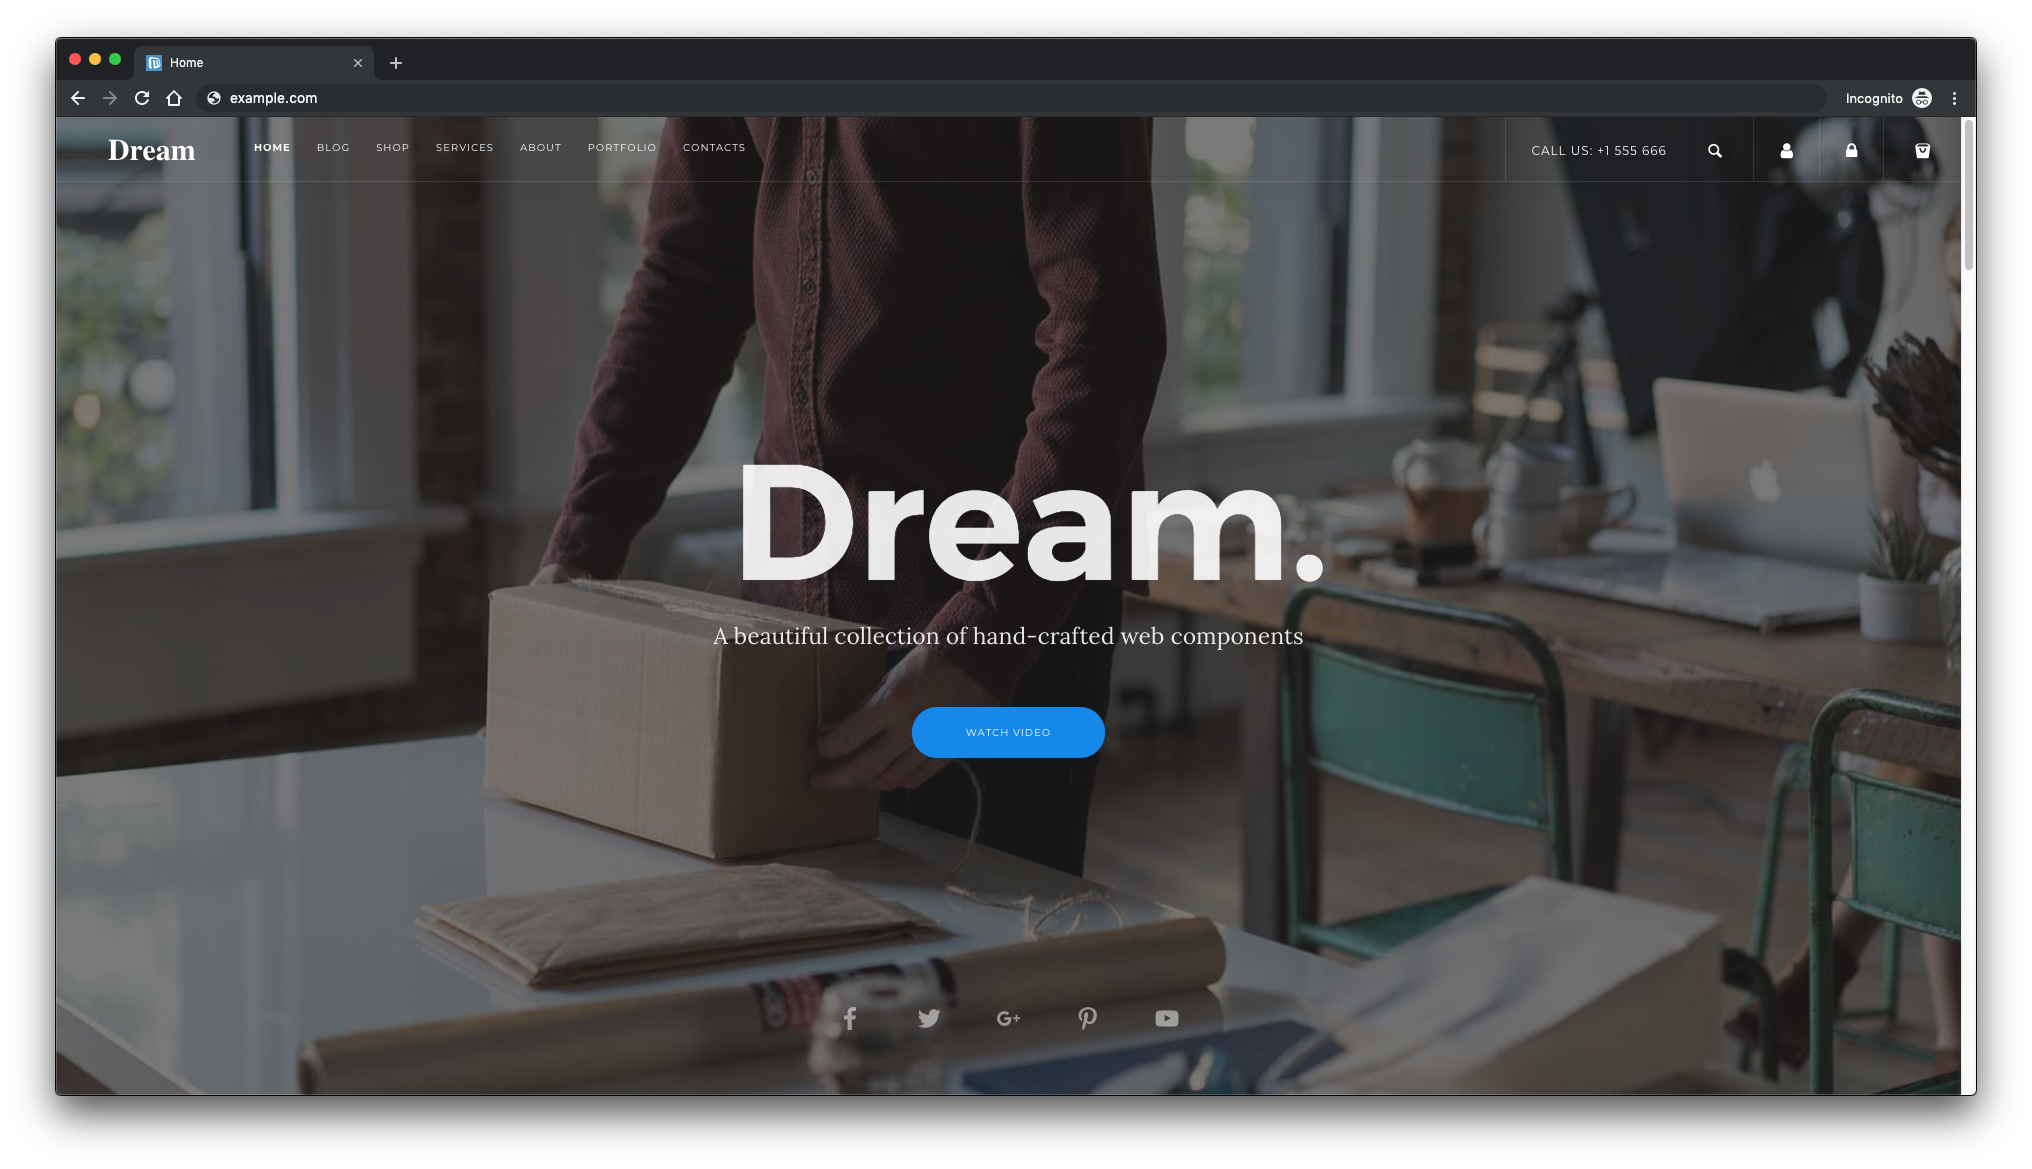
And here is the Microweber frontend:


 Posts

